
Privacy Policy of Secure Vault Usage
These terms define the secure usage, responsibilities, inheritance workflows, and encrypted infrastructure policies governing the Vaultix platform.
Who we are and what this policy covers
Vaultix LLC (Vaultix, we, us or our) provides encrypted information storage and digital-legacy access technology. This Privacy Policy explains how we collect, use, disclose and retain personal information when you visit vaultixsecure.com, use a Vaultix account, act as a designated beneficiary or contact us.
Vaultix LLC is responsible for personal information processed to operate these Services. Our address is the company correspondence address published on our Contact page; privacy requests can be submitted by email without using a postal address. For privacy requests, contact support@vaultixsecure.com and mark your message Privacy Request. Our privacy contact is support@vaultixsecure.com. Details of any legally required local representative or data protection officer will be published on our Contact page for the relevant supported market.
Information and its sources
We receive information directly from account holders, beneficiaries and people contacting us. A person designated as a beneficiary may have their name, email address, telephone number and assignment supplied by the account holder before that beneficiary registers. We also collect activity and security information through operation of the Services and receive payment status and transaction information from Stripe.
| Category | Examples | Purpose |
|---|---|---|
| Account and authentication | Name, email, telephone number, account identifiers, authentication settings and reset events | Account administration, authentication and recovery |
| Vault Content | Uploaded documents, credentials, personal instructions and other encrypted information | Storage and authorized access |
| Beneficiary and workflow | Beneficiary contact details, item assignments, inactivity settings, verification results and release status | Invitations, verification and configured legacy access |
| Billing | Plan, payment status, transaction references and relevant billing details | Payments, refunds, accounting and subscription management |
| Activity and security | Logins, reminder interactions, IP and device information, session and security events | Inactivity workflows, fraud prevention and service security |
| Support | Messages, contact details and information supplied during review | Support, access disputes and privacy requests |
Vault Content can contain personal information about you or other people, including sensitive information if you choose to include it. Upload only what you have the right to store and disclose. Do not send passwords, PINs, wallet private keys or recovery phrases in support messages. Website tracking practices are described in section 10.
Encryption and who can access information
Protected Vault Content is stored in encrypted form. The encryption key is managed through backend infrastructure and is not solely user-managed. Vaultix therefore does not claim that it is technically incapable of decrypting Vault Content or that its service is a zero-knowledge vault. Authorized backend processes may process protected information as needed to provide access and operate the Services.
Reassignment of an encrypted Vault Item does not require a staff member to manually read it. That operational process does not mean there is an architectural guarantee that all plaintext is inaccessible to Vaultix. Account, billing, beneficiary, activity and support information is also processed to operate the service.
Account password and asset PIN resets use the registered email address. Two-factor authentication is available. There is currently no Recovery Contact feature. Protecting your email account is important because it is used for recovery.
How and why we use information
We use personal information to register and authenticate accounts; store and provide access to Vault Content; administer subscriptions and payments; operate reminders, beneficiary verification and reassignment; provide support; manage security and investigate abuse; troubleshoot and maintain the Services; meet legal obligations; and resolve disputes.
Login and activation-reminder interactions help determine whether a configured inactivity workflow progresses. This is an automated assessment of account activity, not a determination of death, incapacity or inheritance rights. Manual review may be used in certain access or verification cases. If you believe an activation is incorrect, contact support immediately.
Providing required account, payment or verification information is necessary for the related feature; if it is not provided, we may be unable to provide that feature. Optional information should be limited to what you want to store or share.
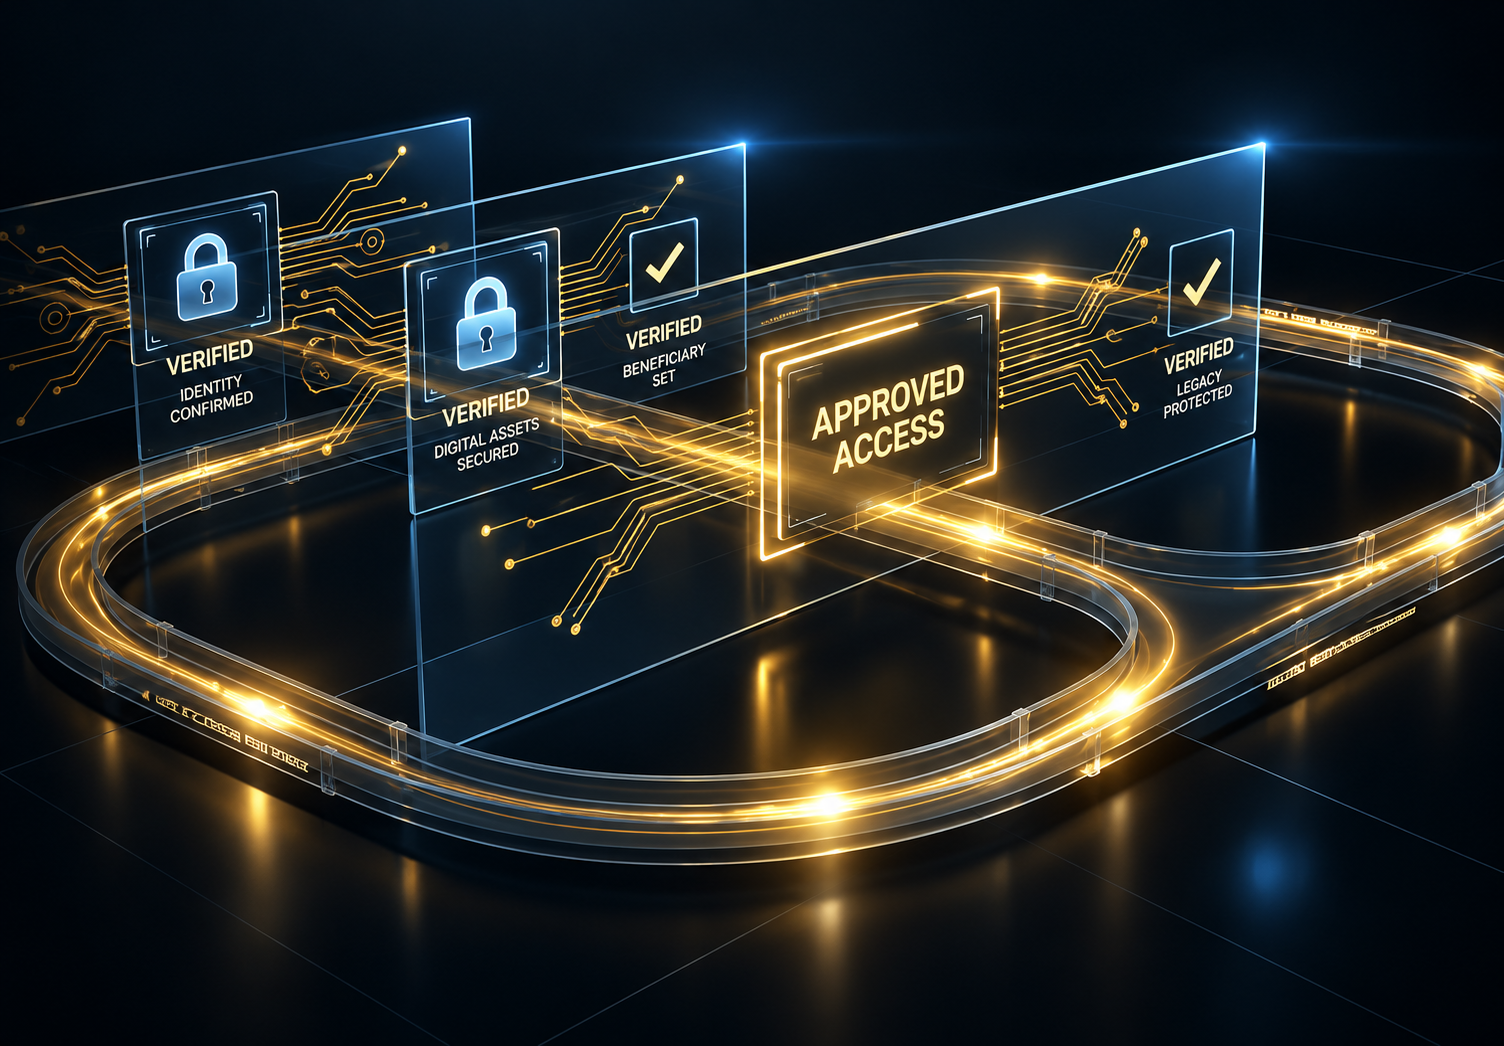
FIG 4.1 — CLIENT-SIDE ENCRYPTION ARCHITECTURE
Legal bases where required
Where applicable law requires a legal basis, we use the basis appropriate to the purpose and the information involved. Account administration, storage and subscription handling generally support performance of our agreement with the account holder. Security, fraud prevention, support, service maintenance and proportionate beneficiary communications may rely on legitimate interests where that basis is permitted and does not override individual rights. Accounting, valid legal requests and other mandatory duties rely on legal obligations. Optional marketing or non-essential tracking uses consent where required.
A contract with an account holder does not automatically provide a lawful basis for all processing of another person’s information. Where law requires consent or another condition for beneficiary information or sensitive content, that condition must be satisfied. Withdrawal of consent does not affect processing lawfully carried out before withdrawal. For sensitive information, including health, religious or similar protected data, we will obtain explicit consent where that is the appropriate and legally required basis, or establish another applicable statutory condition before processing. An account holder cannot give blanket consent on behalf of every person mentioned in a document. If a lawful condition cannot be established, that content must not be uploaded or disclosed. We will apply the applicable Saudi PDPL requirements when processing personal information of people residing in Saudi Arabia, and EEA, UK and other local requirements where those laws apply.
Trigger Activation
User account registers complete cryptographic inactivity beyond the predefined temporal threshold (e.g., 90, 180, or 365 days).
Verification Phase
A mandatory grace period (typically 14–30 days) commences. High-priority, multi-channel alerts are broadcast to the primary User to halt the process if erroneously triggered.
Protocol Execution
Smart contracts execute irrevocably, releasing segmented decryption shards to pre-verified legacy beneficiaries, enabling controlled asset reconstruction.
Beneficiary access and disclosure
We use beneficiary contact details to send invitations or verification messages and operate the assignment configured by the account holder. After the relevant inactivity and verification requirements are satisfied, the whole assigned Vault Item is reassigned within Vaultix to that beneficiary. Information in the item then becomes available to the beneficiary through the service. The beneficiary may download it or continue using Vaultix.
The account holder should consider the information disclosed in an assignment, inform the beneficiary where appropriate and keep the instructions current. Beneficiaries may contact us about their information even before creating an account. Closure of the original account does not automatically erase an item already reassigned to another account or copies downloaded outside Vaultix.
Providers and other recipients
We disclose information to providers to the extent necessary to operate the relevant service. The confirmed providers are AWS for cloud infrastructure and Stripe for payment processing. Stripe processes payment information under the role and terms applicable to the transaction; its own privacy notice also applies to information it processes independently.
Other recipients supporting authentication, email or SMS, analytics, support or security are limited to providers approved for the relevant purpose and listed in a public Service Providers section on our Contact page. That list will identify each provider, its function and processing countries and will be updated before a material new use. We propose limiting the initial stack to AWS hosting and approved email/SMS delivery services, Stripe payments and Vaultix-operated authentication and support. No additional advertising or analytics provider will be enabled without updating the disclosure and providing the required choices. For provider questions, contact support.
We may disclose information where required by law or valid legal process, to investigate fraud or protect legal rights and safety, where you direct us to do so, or in a merger, financing, reorganization or sale subject to applicable safeguards and notice requirements. Disclosures are limited to what is necessary for the relevant purpose.
We do not sell personal information, disclose it for cross-context behavioral advertising, or use Vault Content to train general-purpose AI models. We do not use advertising pixels or remarketing audiences. Necessary provider processing, your instructed beneficiary disclosure and legally required disclosures are distinct from selling personal information. If a future change introduces a use requiring an opt-out or consent, we will provide the legally required disclosure and choice before beginning that use.
Hosting and international processing
Vaultix uses AWS infrastructure, with primary application hosting in Northern Virginia, United States. Personal information may therefore be processed in the United States even if you live elsewhere. The database and backup locations and any replication locations are Northern Virginia, United States, as the proposed default for production databases and backup storage, with no cross-region replication unless separately approved and disclosed. A provider location outside that region will be identified in the published provider list. Other provider locations are identified in section 7.
Cross-border processing is subject to the requirements of the laws applicable to you and to Vaultix. For transfers requiring safeguards, our proposed framework is to use the applicable European Commission Standard Contractual Clauses for EEA transfers, the UK International Data Transfer Addendum or Agreement for UK transfers, and safeguards permitted under the Saudi PDPL transfer regulations, including the applicable Saudi standard clauses where appropriate. We will assess the recipient and transfer risks, apply additional safeguards where needed and enter the necessary arrangements before the relevant processing begins. We will not rely solely on US hosting or a general acceptance of this policy as proof of transfer compliance. You can request information about applicable safeguards at support@vaultixsecure.com. Using Vaultix or accepting this policy is not, by itself, a substitute for a legally required transfer mechanism. We do not promise storage exclusively in your country of residence.
Retention and account deletion
We retain account information and Vault Content while needed to provide the Services. When an account is deleted, the current process is a soft delete: account information and encrypted content remain in the database for a 30-day retention and recovery period rather than being immediately permanently erased. To request restoration during that period, contact support; verification and technical availability apply.
After 30 days, removal of live data and remaining backup copies follows permanent removal from live storage at the end of the 30-day recovery period and expiry or secure removal of backup copies within a further 30 days. The proposed ordinary maximum is 60 days from the deletion request. Backup-only copies are excluded from ordinary restoration and beneficiary release; deletion records are reapplied after disaster-recovery restoration. Legally required records and valid legal holds are treated separately. AWS backups are currently reported as monthly. The frequency of creating backups is separate from how long copies are retained and does not mean deletion occurs immediately or that every recent change can be restored.
and accounting records may be retained for the period required by applicable tax or accounting rules. Security and fraud records are retained for the period reasonably necessary to investigate incidents and protect the Services. Support and dispute records are kept for the period needed to resolve the matter and applicable legal claims. A valid legal hold may extend retention for affected records. We limit retained information to the applicable purpose. Our proposed schedule is seven years after the relevant transaction for accounting and payment records; 12 months from the event for routine security logs; 24 months after resolution for ordinary support matters; and six years after final resolution for access disputes, verified fraud investigations and legal claims, subject to any shorter mandatory limit or longer legal hold. Verification documents, if requested, are removed within 30 days after the verification or related dispute ends, while a minimal record of the verification outcome is retained with the relevant account or dispute record. We review ongoing legal holds annually and remove unnecessary records. These periods do not extend ordinary retention of all Vault Content.
An item already reassigned to a beneficiary is managed under that beneficiary account. Account deletion does not erase downloaded copies held outside Vaultix. Privacy erasure requests are assessed separately under applicable law, including any requirement to act sooner than the ordinary recovery period.
Cookies and website tracking
The website and account service may use cookies or similar technologies to support sign-in, session management and security. Our proposed initial policy is essential cookies only: an authentication/session cookie that expires at sign-out or after 24 hours, a request-security token that expires with its session, and a privacy-preference cookie retained for six months where needed to record a choice. We will not deploy analytics cookies, advertising cookies, pixels or session-replay tools at launch. The Cookie Information section on our Contact page will identify the actual cookie names, provider and durations before publication. We will not enable an optional tracker until that notice and any required consent controls have been updated.
If non-essential analytics or advertising technologies are enabled, their use and available choices must be described in those settings. Where consent is required, those technologies must remain disabled until consent is given, and withdrawal must be available. Browser controls may also let you remove or block cookies, although blocking essential functionality can affect access. We do not treat acceptance of these Terms or this Privacy Policy as consent to optional tracking.
Communications and choices
We send account, security, recovery, reminder, beneficiary and billing messages needed to operate the Services. If promotional communications are offered, you may unsubscribe using the mechanism provided or contact support. Withdrawing marketing permission does not stop necessary service messages. Our proposed marketing policy is opt-in promotional email only, with no preselected consent boxes. Marketing permission is separate from registration, purchase and beneficiary designation. We retain only the minimal suppression record needed to honor an unsubscribe request and remove unused marketing-list entries after 24 months without engagement.
Security measures
12 Security measures Vaultix uses encryption, authentication controls, session management, IP and device monitoring and security logging. Two-factor authentication is available. Login information is available in the account dashboard. The system can prevent login or terminate a session where required for security.
No method of transmission or storage is completely risk-free. These measures are not a guarantee against unauthorized access or data loss. If a personal-data incident occurs, we will make any notifications and take the steps required by applicable law. Do not infer SOC 2, ISO 27001 or other certification from the use of these controls.
Privacy rights and requests
Depending on the law applicable to you, you may have rights to receive information about processing; obtain access or a copy; correct inaccurate information; request deletion; restrict or object to certain processing; receive portable information; withdraw consent; or exercise applicable advertising or sale opt-out rights. Rights and lawful exceptions vary by jurisdiction.
Send requests to support@vaultixsecure.com with Privacy Request in the subject. You may also use supported account settings. We may request proportionate information to verify identity or authority before providing access or acting on a request. Never send a password or PIN. We will respond within the period required by applicable law and explain any refusal or applicable exception.
You may lodge a complaint with the relevant data-protection authority and use any appeal process available under applicable law. Where applicable, authorities include SDAIA in Saudi Arabia, your EEA national data-protection authority, or the UK Information Commissioner. Contacting us first is optional and does not limit that right. We aim to acknowledge requests within five business days and respond within 30 calendar days, or sooner where law requires. Any permitted extension will be explained within the initial statutory period. If a request is declined, you may ask for an internal review by replying with Privacy Appeal; we aim to complete that review within 30 days, subject to any applicable shorter period. This voluntary process does not replace statutory complaint or appeal rights. Where local law provides a sale/sharing opt-out or recognized browser preference, we will honor it for any processing to which that right applies.
Children and third-party information
The Services are intended for people legally capable of entering into the applicable agreement. The minimum age for account holders and beneficiary accounts is 18 years, or the local age of legal majority if higher. A minor may be named in information or future instructions, but cannot receive an independent beneficiary account until eligible. A parent, guardian or trustee is not automatically substituted for a designated minor; the account holder must make a lawful assignment to an eligible adult if earlier access is intended. If you believe a child has created an account or provided information improperly, contact support so we can assess the situation.
An account holder may store documents mentioning family members, including children, only where they have a lawful right to do so. Such information remains subject to this policy and applicable law. Do not assume that designating a minor authorizes an independent account or bypasses a required guardian process.
Policy changes and contact
We will publish updates on this page and revise the last-updated date. For material changes, we will provide any additional notice or consent required by law. An update does not authorize retroactive incompatible use of information.
Privacy enquiries and requests: Vaultix LLC
Email: support@vaultixsecure.com
Address: the company correspondence address published on our Contact page; privacy requests can be submitted by email without using a postal address.

Secure Your Digital Legacy Today
Begin protecting your assets with institutional-grade security. Setup takes minutes, protection lasts generations.